Our information security is certified
When you choose a digital partner, you want to know that its information security is in good shape. Our information security has been verified by an independent audit, and we were awarded ISO/IEC 27001 certification.
ISO/IEC 27001: information security management system
ISO/IEC 27001 is the international standard for information security management. It sets out the requirements for an information security management system. We were certified to the standard (ISO/IEC 27001:2022) in December 2025. The certification shows that we identify our information security risks and manage them systematically. We share our information security management model with our parent company, Liana Technologies, and the certification was carried out by the independent auditor Into Certification.
How does the management system work?
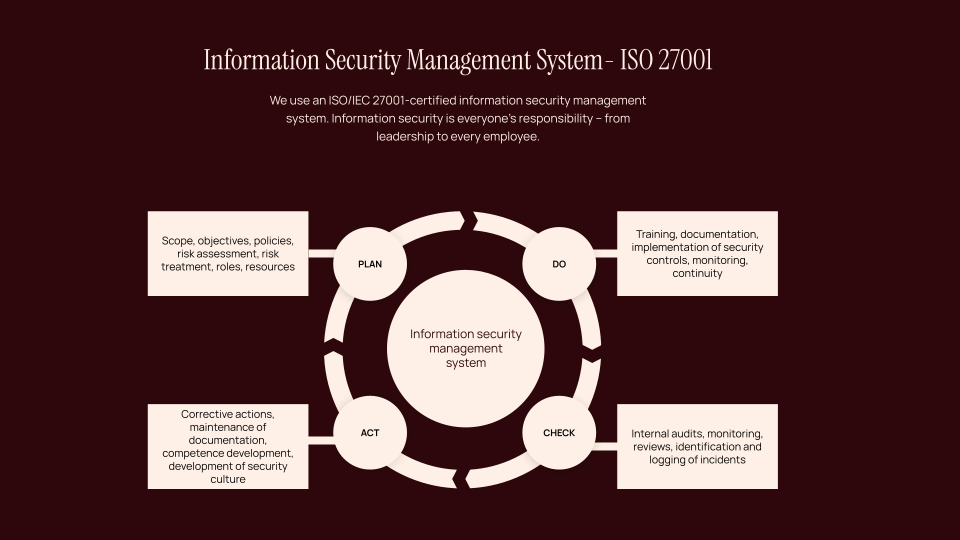
Information security is not a one-off project for us but an ongoing process. We set objectives and practices and identify risks (Plan). We implement them through training, documentation and controls (Do). We check their effectiveness with internal audits and reviews (Check). We correct deviations and develop our skills and security culture (Act). Information security is everyone’s responsibility here, from leadership to every employee.
What does this mean in practice?
- Our leadership is committed to improving information security
- Information security covers all of our work, not just technical operations
- Risks have been identified, and each has a management plan
- The work is ongoing and monitored regularly
This also matters to our clients because of regulation: many of them fall under the EU NIS2 Directive and Finland’s Cybersecurity Act, which implements it nationally. Evermade is not itself directly in scope of the regulation, but as part of our clients’ supply chains, we want to operate in line with its requirements. The certification can also reduce the need for separate security questionnaires when you evaluate your suppliers.
Need more information for your supplier assessment? Contact us and we’ll tell you more.
insights
Don’t close the door on useful AI bots — who’s visiting your website?
When AI shops for you in an online store, the brand matters
AI-generated content labelling becomes mandatory in August
A new cancellation feature is coming to online stores, what does this mean for merchants?
Agent-driven buying is here: How the evolution of the buyer journey is changing e-commerce?
EverTalk: Why every website needs a strategy?
The designer’s role in the AI era
Why WordPress hasn’t been the Enterprise default — And why that’s finally changing
Global Accessibility Awareness Day – small actions, big impact